
In this article
- What Is Annex III Under the EU AI Act
- What Changed With the Digital Omnibus
- The Full EU AI Act Timeline, Not Just the Annex III Date
- Why the Deadline Was Pushed Back
- SME and Small Mid-Cap Relief in More Detail
- What Did Not Change
- Penalties for Getting This Wrong
- Provider vs Deployer: Who Needs to Do What
- How This Affects Your Compliance Planning
- Common Mistakes Businesses Make With the Extended Timeline
- How AnnexOps Helps With This Timeline
- Ready to build your Annex III readiness?
- Related Reading
- Author: Nitin Grover
The EU AI Act Annex III deadline for standalone high-risk AI systems has moved from August 2, 2026 to December 2, 2027. This is a confirmed, binding change under Regulation (EU) 2026/1744, part of the Digital Omnibus on AI. But this delay does not mean businesses can stop preparing, since several other parts of the regulation are already active and enforceable right now.
If your company builds or deploys AI used in hiring, credit scoring, biometric identification, education access, or law enforcement, this date change directly affects your compliance timeline. Here is what actually shifted, what stayed the same, and what you should be doing with this extra time.
This is not a minor procedural update. It reshapes the entire near-term compliance roadmap for thousands of companies across Europe, from large enterprises running biometric verification systems to smaller SaaS teams building AI tools for HR and lending. Understanding exactly what moved, and what did not, is the difference between using this window wisely and getting caught off guard when December 2027 eventually arrives.
This guide covers everything you need to know about the Annex III deadline change. For deeper detail on specific areas, see:
- Annex III Explained: Which AI Systems Are Covered
- Annex III vs Annex I: What’s the Difference
- How to Prepare High-Risk AI Systems Before December 2027
- EU AI Act 2028 Deadline: High-Risk AI in Regulated Products
Getting ready for the Annex III deadline?
AnnexOps helps AI teams classify risk, track obligations, generate documentation, and build audit-ready evidence well before December 2027.
What Is Annex III Under the EU AI Act
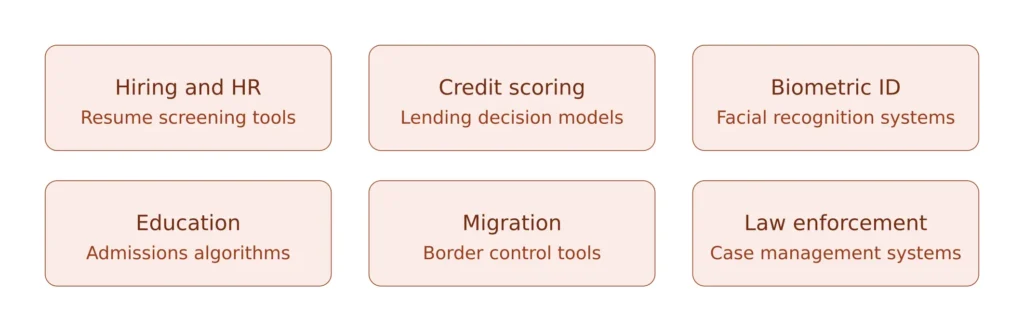
Annex III lists the categories of AI systems that the EU AI Act treats as high risk on their own, without being tied to any other product safety law. This includes AI used for recruitment and employee management, creditworthiness assessment, biometric identification and categorization, access to education and vocational training, migration and border control, and administration of justice.
In practical terms, this covers a wide range of everyday business tools. A resume screening tool that ranks candidates automatically falls here. So does a credit scoring model used by a fintech lender, a facial recognition system used for identity verification, an admissions algorithm used by a university, or a case management tool used by a public authority to assess asylum applications. These are not niche or experimental use cases, they are systems already running inside real businesses today, often without anyone in the company having formally classified them under the Act.
These systems were originally required to meet the full set of high-risk obligations, covering risk management, technical documentation, logging, human oversight, and conformity assessment, by August 2, 2026. That date has now moved to December 2, 2027 for AI systems classified as high-risk under Article 6(2) and Annex III, but the underlying requirements have not been removed; their application has been deferred.
What Changed With the Digital Omnibus
On June 29, 2026, the Council of the European Union gave final approval to the Digital Omnibus on AI, a simplification package that amended the EU AI Act’s timeline. The regulation was published in the Official Journal on July 24, 2026 and entered into force on July 27, 2026, just six days before the original deadline. It is now binding law, not a proposal under discussion.
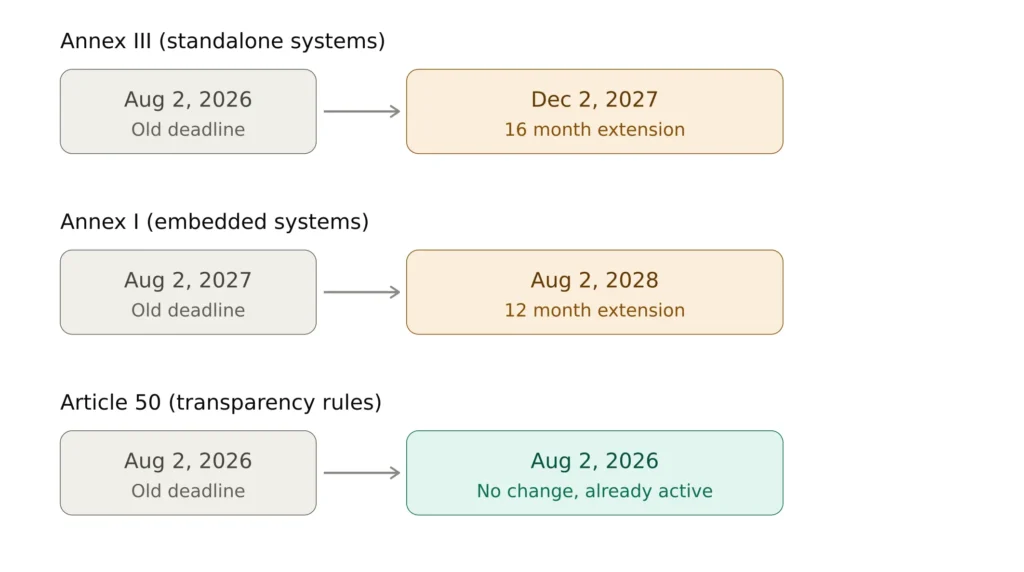
Two dates moved as part of this package. Standalone high-risk systems under Annex III now have until December 2, 2027 to comply, a 16-month extension. AI systems embedded in products already regulated under EU product safety law, covered under Annex I, such as AI inside medical devices or industrial machinery, now have until August 2, 2028, a 12-month extension.
Getting here was not a quick or simple process. The European Commission first published the Digital Omnibus proposal on November 19, 2025. The European Parliament endorsed the package on June 16, 2026 with a 423 to 57 vote, and the Council of the European Union gave final approval on June 29, 2026. Throughout this period, the original August 2026 deadline technically remained the legally binding date, since the amendment only took effect once formally adopted and published. This meant companies had to keep preparing against the original timeline right up until the very last weeks, which created real uncertainty for compliance and legal teams trying to plan budgets and headcount around a moving target.
The Full EU AI Act Timeline, Not Just the Annex III Date
It helps to see the Annex III change alongside every other milestone in the Act, since businesses often confuse one deadline for another. The EU AI Act does not apply all at once, it rolls out in stages, and each stage covers a different set of obligations.
Prohibited AI practices and the AI literacy requirements under Article 4 began applying from February 2, 2025. These cover AI uses considered unacceptable, such as certain manipulative or exploitative systems, and the duty of organizations to ensure staff have a reasonable understanding of the AI tools they work with.
General-purpose AI obligations followed on August 2, 2025, covering providers of foundation models and large language models, including transparency and copyright-related duties. Models placed on the market before that date have a later compliance point of August 2, 2027.
August 2, 2026 brought the broader enforcement phase, along with Article 50 transparency obligations. This is also when the AI Office and national authorities gained enforcement powers over the provisions applicable at that stage.
From December 2, 2026, additional prohibited AI practices introduced through the 2026 amendments, including the relevant prohibitions concerning the generation or manipulation of non-consensual intimate material and child sexual abuse material, will apply.
December 2, 2027 is the Annex III milestone this guide is centered on, when standalone high-risk AI systems must meet the full set of obligations.
August 2, 2028 is the application date for the Chapter III Sections 1–3 high-risk AI rules for systems classified as high-risk under Article 6(1) and Annex I, including relevant AI systems embedded in products covered by EU harmonisation legislation.
Reading the timeline this way makes it clear that Annex III is one milestone among several, not the only date that matters. A business could be fully compliant with the December 2027 requirement and still be in breach of an Article 50 transparency duty that has applied since August 2026.
Why the Deadline Was Pushed Back
The delay was driven mainly by the fact that harmonised technical standards needed to support compliance were not ready in time. The European standardisation bodies responsible for drafting the detailed technical requirements that businesses would need to follow, covering areas like risk management documentation formats and conformity assessment procedures, had not finished this work by the original deadline. Without these standards in place, companies would have been expected to build compliance programs based on incomplete guidance, increasing both cost and legal uncertainty.
Businesses and regulators both raised concerns that companies would be expected to meet obligations without clear technical guidance on how to actually do it. Industry groups across the EU lobbied for more runway, arguing that rushing implementation without proper standards would lead to inconsistent compliance approaches across member states, undermining the very goal of having a single harmonised regulation. The Digital Omnibus also extended certain existing regulatory relief measures from SMEs to small mid-cap enterprises (SMCs). Under the EU definition, an SMC is an enterprise that is not an SME, employs fewer than 750 people, and has annual turnover of no more than €150 million or an annual balance-sheet total of no more than €129 million.
SME and Small Mid-Cap Relief in More Detail
The size-based relief deserves its own explanation, since it applies differently depending on company size. For classic SMEs, meaning companies with fewer than 250 employees and under €50 million in annual turnover, the Digital Omnibus allows simplified technical documentation formats and lighter conformity assessment procedures, recognizing that a small company building one AI product does not have the same resources as a large enterprise running dozens of systems.
For small mid-cap companies, a newly formalized category covering businesses with fewer than 750 employees and under €150 million turnover, the relief is narrower but still meaningful, mainly affecting documentation depth rather than removing entire obligations.
This distinction matters for planning purposes. A small AI startup building a single hiring tool should not assume its compliance burden is identical to that of a large enterprise SaaS platform with the same tool integrated into ten different products. Understanding which size category a business falls into is one of the first practical steps in scoping the actual work ahead.
What Did Not Change
This is the part most businesses overlook. The December 2027 and August 2028 extensions specifically change the application dates for the Chapter III Sections 1–3 high-risk AI rules covered by Article 6(2)/Annex III and Article 6(1)/Annex I respectively. They do not postpone the entire EU AI Act. It did not touch Article 50, the transparency chapter of the Act, which has applied since August 2, 2026 exactly as originally planned. The Article 50 transparency requirements also remain relevant. Depending on the AI system and the applicable provision, providers may have obligations relating to informing people when they are interacting with AI and to making synthetic audio, image, video or text content detectable or appropriately marked.
The overall structure of the Act also stayed intact. The four-tier risk classification system, the conformity assessment regime, and the AI Office’s oversight role are all unaffected by this delay. A new prohibition on AI-generated non-consensual intimate imagery and child sexual abuse material was also added, and this too is not part of the deferral.
Article 4 has also been amended. Rather than maintaining the original direct obligation on providers and deployers, the amended provision requires the Commission and Member States to encourage providers and deployers to take measures that foster sufficient AI literacy among staff and other persons operating or using AI systems on their behalf. Quality management system requirements for high-risk providers, while formally tied to the Annex III deadline, are still worth building early since they take considerable time to put in place properly and rushing them close to a deadline rarely produces a system that actually works well in practice.
Penalties for Getting This Wrong
Moving the Annex III application date does not mean that organizations can ignore the AI Act’s enforcement framework. Once the applicable high-risk obligations become enforceable for a system, non-compliance can result in significant administrative fines under Article 99, subject to the applicable rules and circumstances. Non-compliance with high-risk obligations can still result in fines reaching into the tens of millions of euros or a significant percentage of a company’s global annual turnover, whichever is higher, once the obligations become enforceable.
For businesses that treat December 2027 as a distant date rather than a firm deadline with real consequences attached, the financial exposure only grows the longer proper systems stay unbuilt.
Provider vs Deployer: Who Needs to Do What
One of the most common points of confusion is that the EU AI Act does not place the same obligations on every organization involved with an Annex III AI system. The applicable requirements depend on the organization’s role in relation to the specific AI system. An organization may act as a Provider, a Deployer, or potentially both, depending on the system and how it is developed, placed on the market, or used.
A Provider is a natural or legal person, public authority, agency, or other body that develops an AI system or has an AI system developed and places it on the market or puts it into service under its own name or trademark. Providers of high-risk AI systems have significant obligations relating to areas such as risk management, technical documentation, quality management, conformity assessment, record keeping, and, where applicable, registration in the EU database. The specific obligations depend on the AI system’s classification and circumstances.
A Deployer is a natural or legal person, public authority, agency, or other body that uses an AI system under its authority, except where the use is for a personal non-professional activity. For example, a company that uses a third-party AI recruitment tool to support candidate screening may act as the Deployer of that system. Depending on the AI system and its use, deployers may have obligations relating to using the system according to applicable instructions, assigning human oversight, monitoring its operation, keeping required records, and complying with other applicable requirements under the EU AI Act. Certain deployer obligations may also include informing affected individuals or providing other information where the Act specifically requires it.
A single company can be a Provider for one AI system and a Deployer for another. For example, a SaaS company that develops and places its own AI-powered credit scoring system on the market may be the Provider of that system. If the same company uses a separate third-party AI recruitment system internally, it may act as the Deployer of that system.
How This Affects Your Compliance Planning
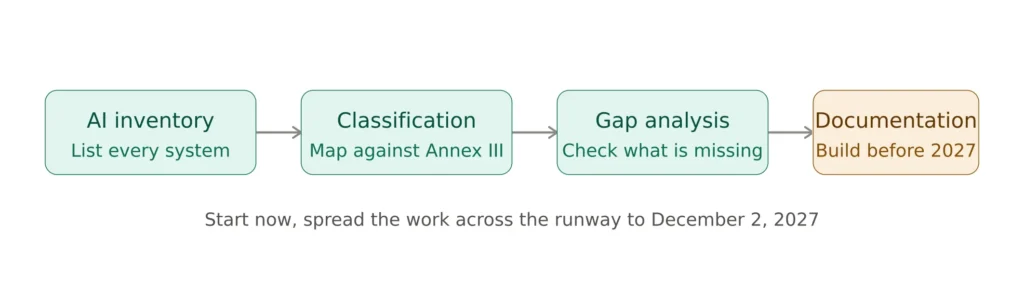
Having until December 2027 does not mean the work should wait until then. Organizations should use the additional time to identify applicable AI systems, determine their roles, assess risk, map obligations, and build the governance, documentation and monitoring processes they will need when the high-risk requirements become applicable.
A practical starting point for most businesses is a proper AI system inventory. Many companies genuinely do not have a complete list of every AI tool running across their departments, especially where individual teams have adopted tools independently without going through a central procurement or legal review process. Without this inventory, it is impossible to know which systems even fall under Annex III in the first place, let alone plan the documentation work needed to support them.
From there, the natural next step is risk classification, mapping each system against the Annex III categories, followed by gap analysis to see how far current documentation and oversight practices are from what the Act will eventually require. Building this incrementally over the next year and a half, rather than compressing it into the final months before December 2027, tends to produce stronger, more defensible compliance records, and gives legal and technical teams enough time to actually understand the systems they are documenting rather than rushing through a checklist.
Businesses that treat this extension as a properly resourced planning window, rather than as permission to delay, will be in a much stronger position when December 2027 arrives. This mirrors what many companies experienced during the early GDPR rollout, where organizations that started preparation well ahead of the enforcement date ended up with far more manageable, lower-stress compliance programs than those that waited until the final months.
Common Mistakes Businesses Make With the Extended Timeline
A few patterns show up repeatedly among companies reacting to this deadline change, and it is worth naming them directly so they can be avoided.
The first is treating the delay as a reason to stop tracking AI systems altogether. Some teams paused their inventory and classification work entirely once news of the extension spread, assuming there was nothing urgent left to do. This overlooks the fact that Article 50, Article 4, and GPAI obligations are already active, and that Annex III work started early is genuinely easier and cheaper than work started under deadline pressure.
The second is confusing the Annex III delay with a delay to the entire Act. As covered earlier, only two specific parts of the regulation moved, everything else continues on its original schedule. Businesses that assume “the AI Act got pushed back” broadly are likely to miss obligations that are already enforceable today.
The third is misclassifying provider and deployer roles, or skipping that classification step entirely. Without knowing which role applies to which system, it becomes impossible to correctly scope what documentation or oversight process is actually required, and this usually surfaces as a costly correction later rather than a small early fix.
The fourth is underestimating how long proper documentation and risk management processes take to build well. Sixteen months sounds like a long runway, but for a company with a dozen or more AI systems across different departments, building a genuinely defensible compliance program in that time requires starting soon, not waiting for year two of the window.
How AnnexOps Helps With This Timeline
AnnexOps gives businesses a centralized platform for AI system discovery, risk classification, Provider/Deployer role classification, obligation management, documentation, evidence management and compliance monitoring. This can help teams organize their preparation for applicable AI Act requirements and the upcoming Annex III milestone. It handles risk classification, generates the required technical documentation, and keeps an audit ready evidence trail as your systems evolve, so the runway to December 2027 gets used to build real compliance infrastructure, not just to postpone the conversation.
AnnexOps is designed to connect AI compliance activities with the broader AI development and deployment lifecycle, helping teams maintain compliance information and evidence as AI systems evolve, rather than depending on someone remembering to run a manual review months later. For companies that already have several Annex III candidate systems running today, this kind of continuous tracking removes much of the guesswork around what still needs attention before the 2027 deadline lands.
Learn how AnnexOps helps AI-driven companies manage EU AI Act compliance with clarity and confidence.
Explore AnnexOps: https://annexops.com/
Ready to build your Annex III readiness?
AnnexOps helps AI teams assess risk, manage compliance obligations, generate documentation, and build audit-ready evidence.
Related Reading
- Annex III Explained: Which AI Systems Are Covered
- Annex III vs Annex I: What’s the Difference
- What Companies Can Do Before the 2027 High-Risk AI Deadline
- EU AI Act High-Risk AI Compliance: 2026 vs 2027
- How to Prepare High-Risk AI Systems Before December 2027
- EU AI Act 2027 Deadline: What AI Providers and Deployers Should Do Now
- EU AI Act 2028 Deadline: High-Risk AI in Regulated Products Explained
Author: Nitin Grover
Nitin Grover is an AI compliance strategist and writer focused on EU AI Act compliance, AI governance, Annex IV documentation, AI risk management, and AI compliance operations for AI startups, SaaS companies, and enterprise AI teams across Europe.
[…] This article breaks down exactly which systems fall under Annex III, with real examples, so you can quickly check whether your AI system is in scope. For the full timeline and what changed with the 2027 deadline, see our complete guide to the Annex III deadline. […]
[…] Standards work in areas such as cybersecurity continues, so organisations should check for updates rather than assume that the current set of standards is complete. Under the amended application timetable, the relevant high-risk AI system requirements in Chapter III, Sections 1 to 3, apply from 2 December 2027 to systems classified as high-risk under Article 6(2) and Annex III, and from 2 August 2028 to systems classified as high-risk under Article 6(1) and Annex I. Other AI Act obligations have different application dates. See our Annex III deadline guide. […]
[…] Die Normungsarbeiten in Bereichen wie Cybersicherheit werden fortgesetzt. Organisationen sollten deshalb aktuelle Entwicklungen überprüfen, statt davon auszugehen, dass der bestehende Normensatz bereits vollständig ist. Nach dem geänderten Zeitplan für die Anwendung gelten die einschlägigen Anforderungen an Hochrisiko-KI-Systeme aus Kapitel III, Abschnitte 1 bis 3, ab dem 2. Dezember 2027 für Systeme, die gemäß Artikel 6 Absatz 2 und Anhang III als Hochrisiko-KI-Systeme eingestuft werden, sowie ab dem 2. August 2028 für Systeme, die gemäß Artikel 6 Absatz 1 und Anhang I als Hochrisiko-KI-Systeme eingestuft werden. Für andere Verpflichtungen aus dem EU AI Act gelten abweichende Anwendungszeitpunkte. Weitere Informationen finden Sie in unserem Leitfaden zur Frist für Anhang III. […]
[…] Article 15 requires high-risk AI systems to achieve an appropriate level of accuracy, robustness and cybersecurity. In our reading, that is a requirement on the AI system, while ISO 27001 certifies an organisation’s information security management system. For high-risk AI systems EU AI Act rules apply from 2 December 2027 for Annex III and 2 August 2028 for Annex I, as set out in our Annex III deadline guide. […]